Skip to content

Experts in hybrid offensive
security.

Hybrid offensive security combines AI agents with human specialists to identify, validate and exploit vulnerabilities continuously, at a speed and coverage a traditional pentest can't reach.

Trusted by

  • Voidr
  • Shelmia
  • Cabacua
  • Criptala
  • Fixed
  • Luna
  • Lexart
  • Houlak

What makes Rekon different?

ARGUS thinks like an attacker and strikes with the force of thousands.

Attackers already use AI, and your defense has to use it too. Far more than a scanner, ARGUS is our proprietary AI-powered pentesting software.

  1. Massively Multi-Agent Architecture

    Thousands of agents, in parallel.

    Deploys thousands of offensive agents working the target at the same time.

  2. Goal-Driven Offensive Reasoning

    Reasons like an attacker.

    Pursues concrete objectives: reaching sensitive data, taking over an account, touching a critical asset.

  3. Dynamic Attack Chaining

    Chains flaws into real attacks.

    Combines multiple weaknesses into attacks no single finding would reveal.

  4. Autonomous PoC Generation

    Impact proven, not assumed.

    Delivers a reproducible proof with the steps, payloads and evidence of compromise.

Explore ARGUS
./argus.
  1. Specialized Hacking Agents

    Each agent is trained on a specific capability: reconnaissance, exploitation, evasion, credentials or privilege escalation.

  2. Collaborative Attack Intelligence

    Agents share findings and build on each other's results to push the attack forward.

  3. Autonomous Attack Planning

    Defines and rewrites its strategy from what it discovers inside the environment.

  4. Adaptive Exploitation

    Adjusts payloads, techniques and attempts in real time to how the system responds.

  5. Parallel Attack Exploration

    Tests thousands of hypotheses and possible entry paths at once.

  6. Novel Vulnerability Discovery

    Surfaces logic flaws and combinations that no rule or signature covers.

  7. Controlled Real-World Exploitation

    Actually exploits the vulnerabilities, inside safe and authorized limits.

  8. Collective Learning

    Every agent builds on what the whole operation learned to make later decisions sharper.

  9. Industry-Adaptive Offensive Intelligence

    Agents are trained on each industry's context, stack, processes and threats, so they think and attack like a specialized adversary.

Every step is supervised by a human.

ARGUS proposes, chains and accelerates. Every intrusive action passes through a person before it runs: the operator authorizes, limits the impact and signs the result.

REKON solutions

01 / Our specialty

REKON Pentesting

We emulate the behavior of a real attacker to detect vulnerabilities.

ARGUS accelerates exploration and reconnaissance, while our specialists execute each PoC to determine impact-based priorities and remediation actions.

02 / Continuous monitoring

REKON Pulse

We monitor every infrastructure change and alert you to known vulnerabilities, patches and new CVEs that may affect your system, keeping your security aligned with everyday needs.

Explore REKON Pulse

03 / Human readiness

REKON Phishing

Preparation of authorized simulations, campaign review and customization, on-demand monitoring at your preferred level of detail, and traceable results to strengthen your team’s knowledge.

Explore REKON Phishing

What can we test?

If it exists, we can test it.

ARGUS evaluates the organization's security the way a real attacker would, deploying offensive agents specialized and adapted to its industry to identify, exploit and chain vulnerabilities within the authorized environment. It covers:

What we can assess

  • External Attack Surface

    What is exposed?

    Domains, apps, APIs, infrastructure and services exposed to the internet.

  • Internal Infrastructure

    What connects your systems?

    Internal networks, servers, endpoints and corporate systems.

  • Web & API Security

    What does your application allow?

    Technical vulnerabilities and business-logic flaws.

  • Cloud Environments

    How is your cloud configured?

    Configurations, identities, permissions, workloads and storage.

  • Identity & Access

    Who can access what?

    Credentials, privileges, Active Directory and lateral movement between accounts.

How we put it to the test

  1. Attack Path Validation

    Paths from the entry point to critical assets.

  2. Industry-Specific Testing

    Scenarios adapted to the business, its stack and its threat landscape.

  3. Controlled Exploitation

    Safe exploitation within the scope and limits agreed up front.

  4. Remediation Validation

    Fresh tests to confirm the gaps were actually closed.

You define the limits. We test how far an attacker can get.

What can you expect when you work with Rekon?

The report connects the flaw to its consequence.

Your team gets reproduction steps and remediation actions. Leadership gets the impact and priority explained. What was not tested is documented too.

Inside a pentest report ↗

Synthetic example · not a real finding

A session accesses another organization's object.

Proof
Identity A → object B → unauthorized access.
Remediation
Check object ownership on every access.
Limit
Demonstration identities and data only.

Attack Path Mapping

See how they could compromise your company

We map the routes an attacker would take from the first entry point to your most critical assets.

Proof of Concept Generation

Get hard evidence, not alerts

Every confirmed finding ships with a reproducible PoC showing how it was exploited and what access it granted.

Exploitability-Based Prioritization

Focus resources on what actually matters

We rank gaps by proven exploitability and impact, so your team knows exactly what to fix first.

Business Impact Analysis

Understand what each gap means for the business

We turn technical findings into plain consequences: data exposure, account takeover, fraud or operational disruption.

Actionable Remediation Guidance

Get a concrete path to close every gap

Each finding comes with its root cause and specific remediation actions, so the owning team can move fast.

Automated Retesting

Verify the fixes actually worked

Once improvements ship, ARGUS reruns the attacks to verify the gaps are effectively closed.

Technical & Executive Reporting

Communicate results to the whole organization

Detailed evidence for technical teams and a clear executive view for leadership, audit, clients and board.

Industry-Adaptive Offensive Intelligence

Test against threats relevant to your business

Agents adapt their strategy to your industry, infrastructure, operations and specific risks.

MITRE ATT&CK Mapping

Understand the real techniques an adversary would use

We map every executed attack to the real-world tactics and techniques of the MITRE ATT&CK standard.

Remediation Validation

Get certainty the risk went down

We don't stop at identifying problems: we verify with evidence that attack paths are actually severed.

Who are we?

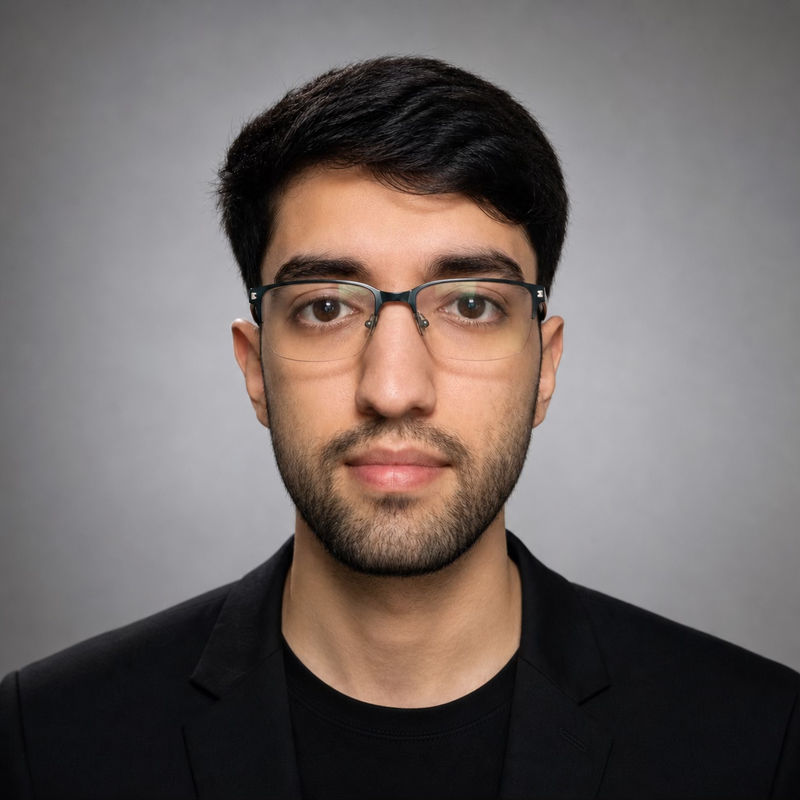
Federico Segredo

CEO

Federico Segredo

Federico built his career around understanding how to make large organizations work better: automation, product, operations, integrations and data. At Tiendamia and PedidosYa he worked leading robotic process automation initiatives, redesign and optimization of operational processes, reductions in production times and improvements to critical KPIs. Fede eliminates manual tasks, reduces friction points and takes operational improvements to scale.

His differentiator is understanding an operation from end to end, finding where the bottleneck really is and turning it into an opportunity for improvement. He combines business vision, technology and an obsession with execution. At Rekon he applies that ability to turn ARGUS into a product, define the strategy and build a company capable of scaling.

LinkedIn
Federico López

CTO

Federico López

Ethical hacker, developer and responsible for creating ARGUS, our proprietary offensive cybersecurity software. He started programming and getting into hacking at 15, and turned the obsession into an exceptional ability to understand systems, find their weak points and build tools to exploit them.

LinkedIn

Frequently asked questions

What does an engagement cover?

External attack surface, internal infrastructure, web applications and APIs, cloud environments and identity. Scope is fixed in writing before we start. Anything found outside scope gets reported, not exploited.

What do I receive at the end?

A report signed by the person who supervised the test: validated findings, reproducible PoCs, MITRE ATT&CK mapping and priority by real impact, not scanner score. The delivery window is fixed in the contract.

How do I verify a finding?

Every finding documents conditions, steps and evidence. We state when risk or scope limits exploitation. A failed attempt does not prove the absence of vulnerabilities: we distinguish confirmed results, inconclusive tests and verified controls.

Is a retest included?

Retest scope and conditions are agreed in the contract. We repeat the agreed cases and document whether the fix works, the finding persists or the test remains limited.

What would an attacker do if they found you today?

Tell us what you need to validate. We start with context and agree on scope before testing.

Do not include credentials or sensitive information. Read our privacy policy.

hello@rekon.sh